New DoD cloud security requirements coming Tuesday

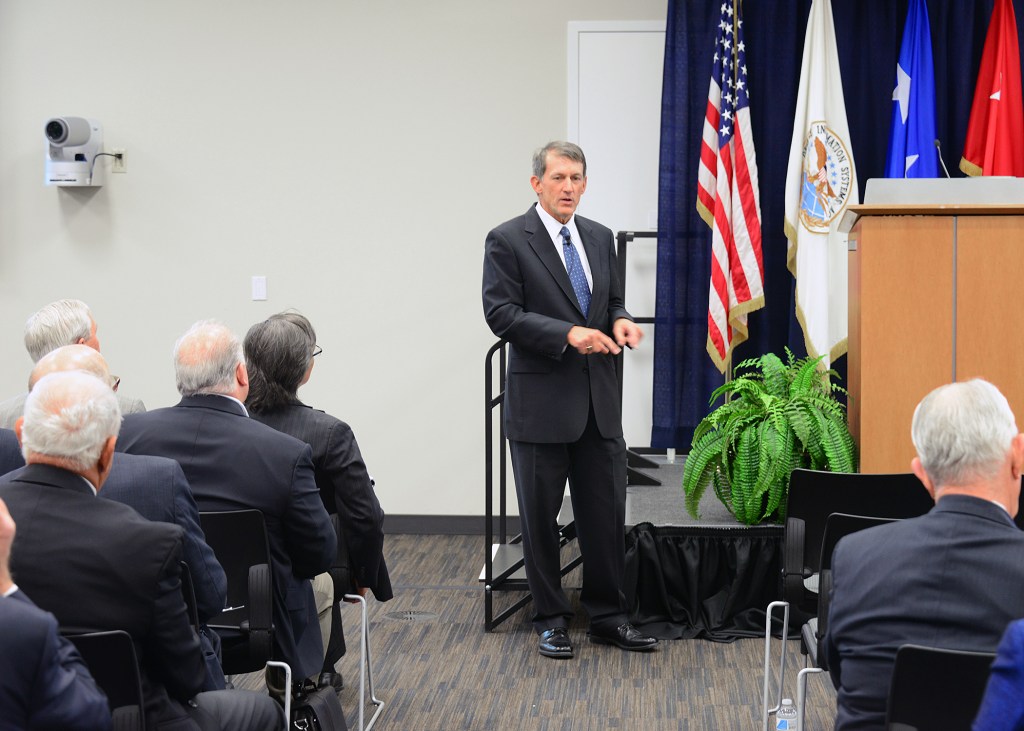
Mark Orndorff, mission assurance executive Defense Information Systems Agency (DISA) at Fort George G. Meade, Md., speaks to a packed audience at DISA during the Forecast to Industry day, August 20, 2014. Orndorff discussed the cyber workforce and how the agency can deliver the capabilities they need to see and defend the network. (U.S. Department of Defense photo by Thomas Burton/Released)

The Defense Information Systems Agency (DISA) is poised to release final security guidance for purchasing cloud services on Tuesday, Jan. 13, as the Defense Department shifts to commercial providers.

Update: Read the follow-up story

After receiving more than 800 comments on the draft guidelines, DISA reorganized the security levels to allow certain work areas to exist in virtual private networks while still keeping the most sensitive data physically separated on DoD networks.

The final draft also tweaks the authorization requirements to track closer to the Federal Risk and Authorization Management Program (FedRAMP) except in specific areas where greater security assurance is needed.

Read the full story at FederalTimes.com.
About 

Aaron Boyd is an awarding-winning journalist currently serving as editor of Federal Times — a Washington, D.C. institution covering federal workforce and contracting for more than 50 years — and Fifth Domain — a news and information hub focused on cybersecurity and cyberwar from a civilian, military and international perspective.